
Due Diligence Software
Hidden relationships jeopardize security.
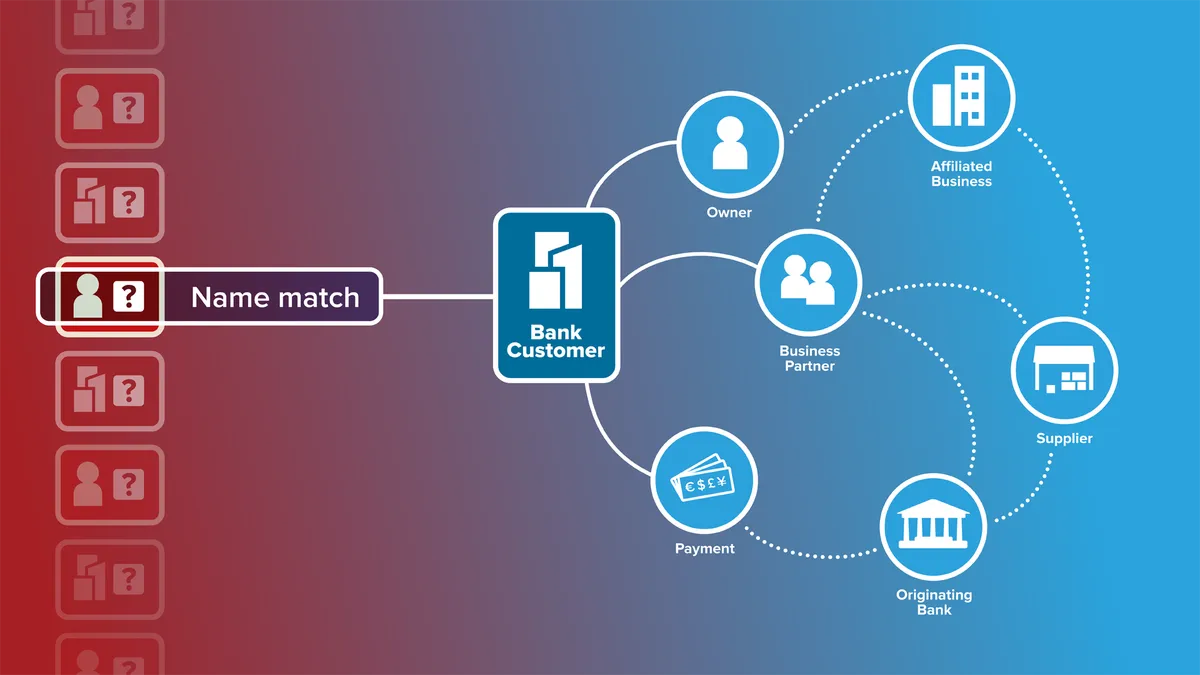
Every individual and organization carries a network of unreported relationships, which may influence or compromise them.
Quantifind helps public-sector teams rapidly assess vendors, partners, landowners, and other entities by applying advanced network analysis to global open-source and commercial data sources. The easy-to-use platform automates due diligence and flags operational, financial, or national-security risks before they reach your supply chain or take root in critical relationships.
200+
global public and commercial data sources
>$16M
federal R&D investment received between 2022-2026
95%
reduction in false positives
100%
auditable, explainable decisions
the problem
Manual review was built for a slower world.
Risk doesn't live in a single name; it hides in networks, aliases, shell companies, and subsidiaries designed to blend in. And a risk profile isn't static. It evolves as owners, investors, and relationships change. One-time screenings and shortlist sampling won't catch that. You have to watch everything.
the fix
Batch screening with Quantifind enables even small teams to perform thorough, continuous vetting.
The Capability Stack
Six capabilities. One diligence workflow.
Entity Screening
Vendor and subcontractor screening with Name Science™ entity resolution at 95%+ accuracy, run across a full population in batch or in real time for a single award.
Beneficial Ownership & FOCI Risk
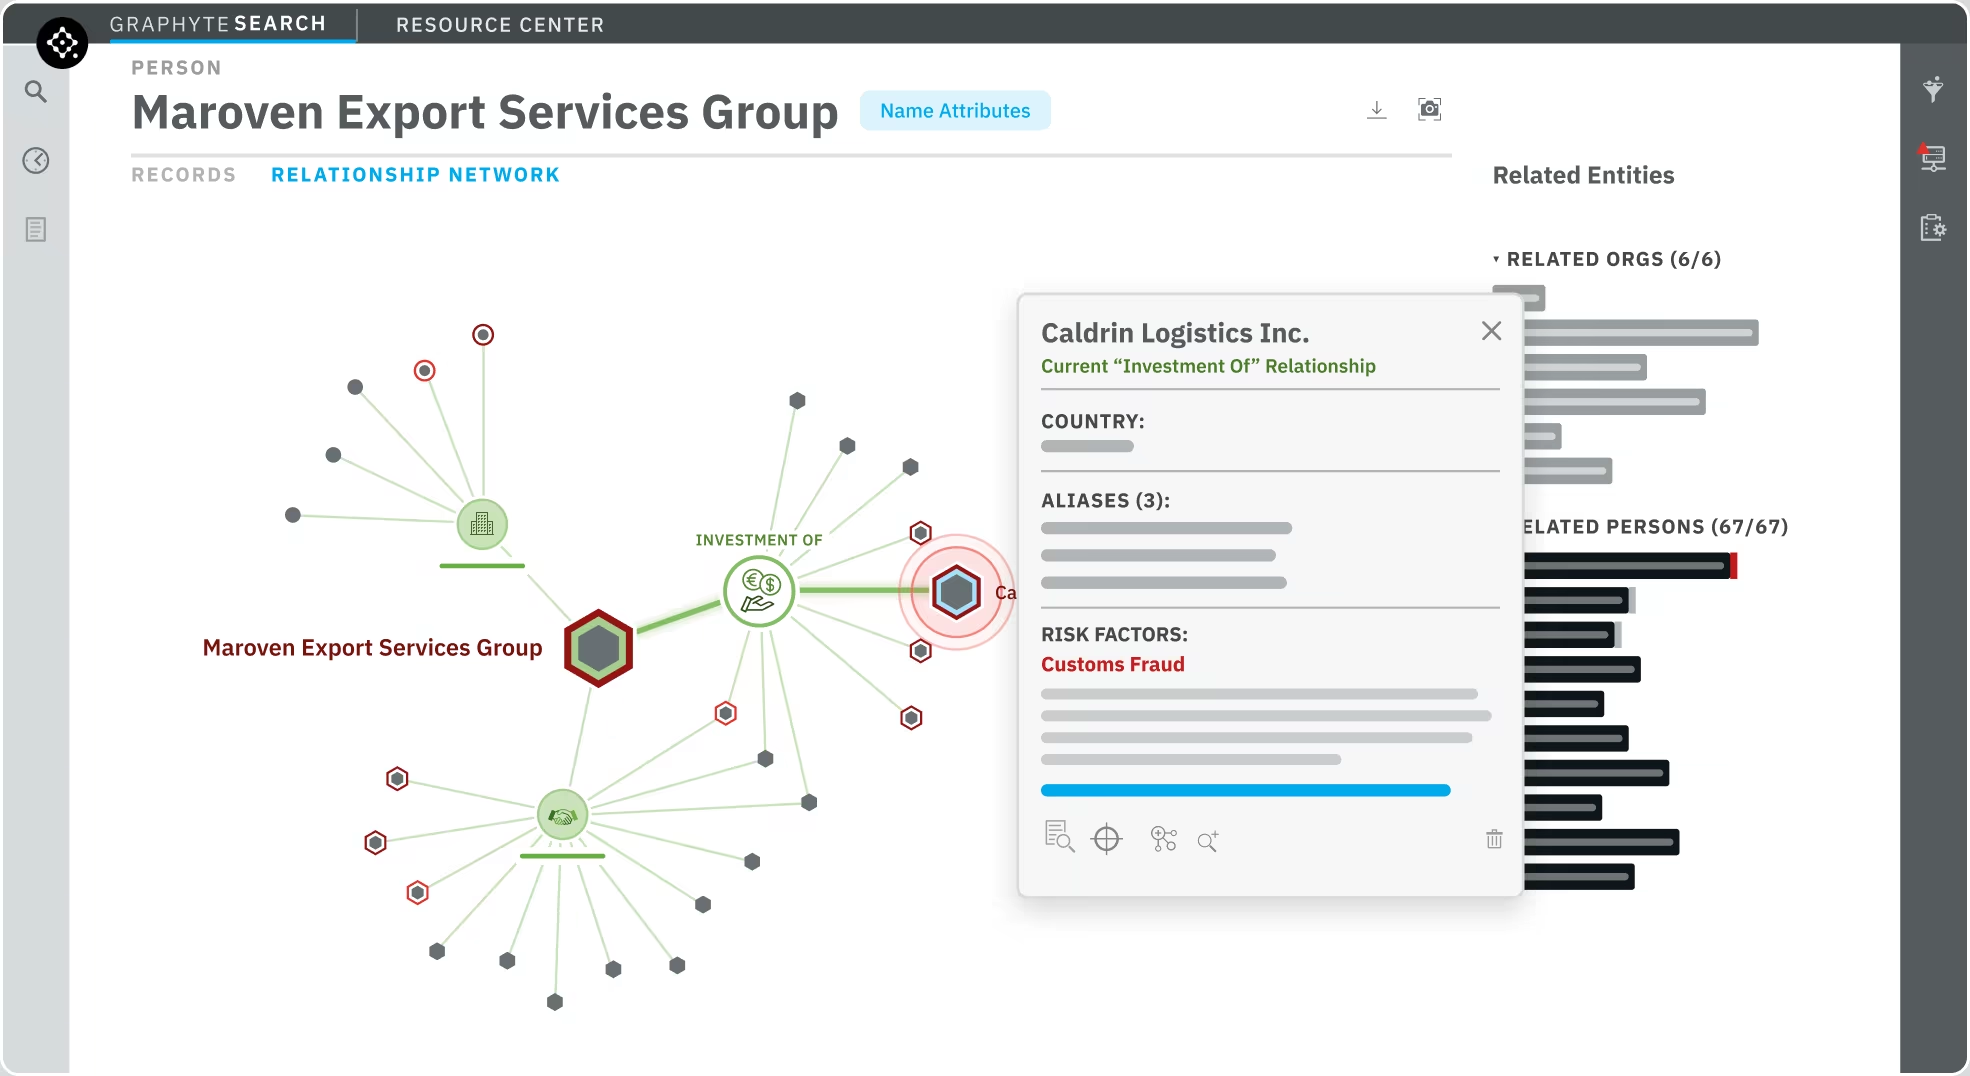
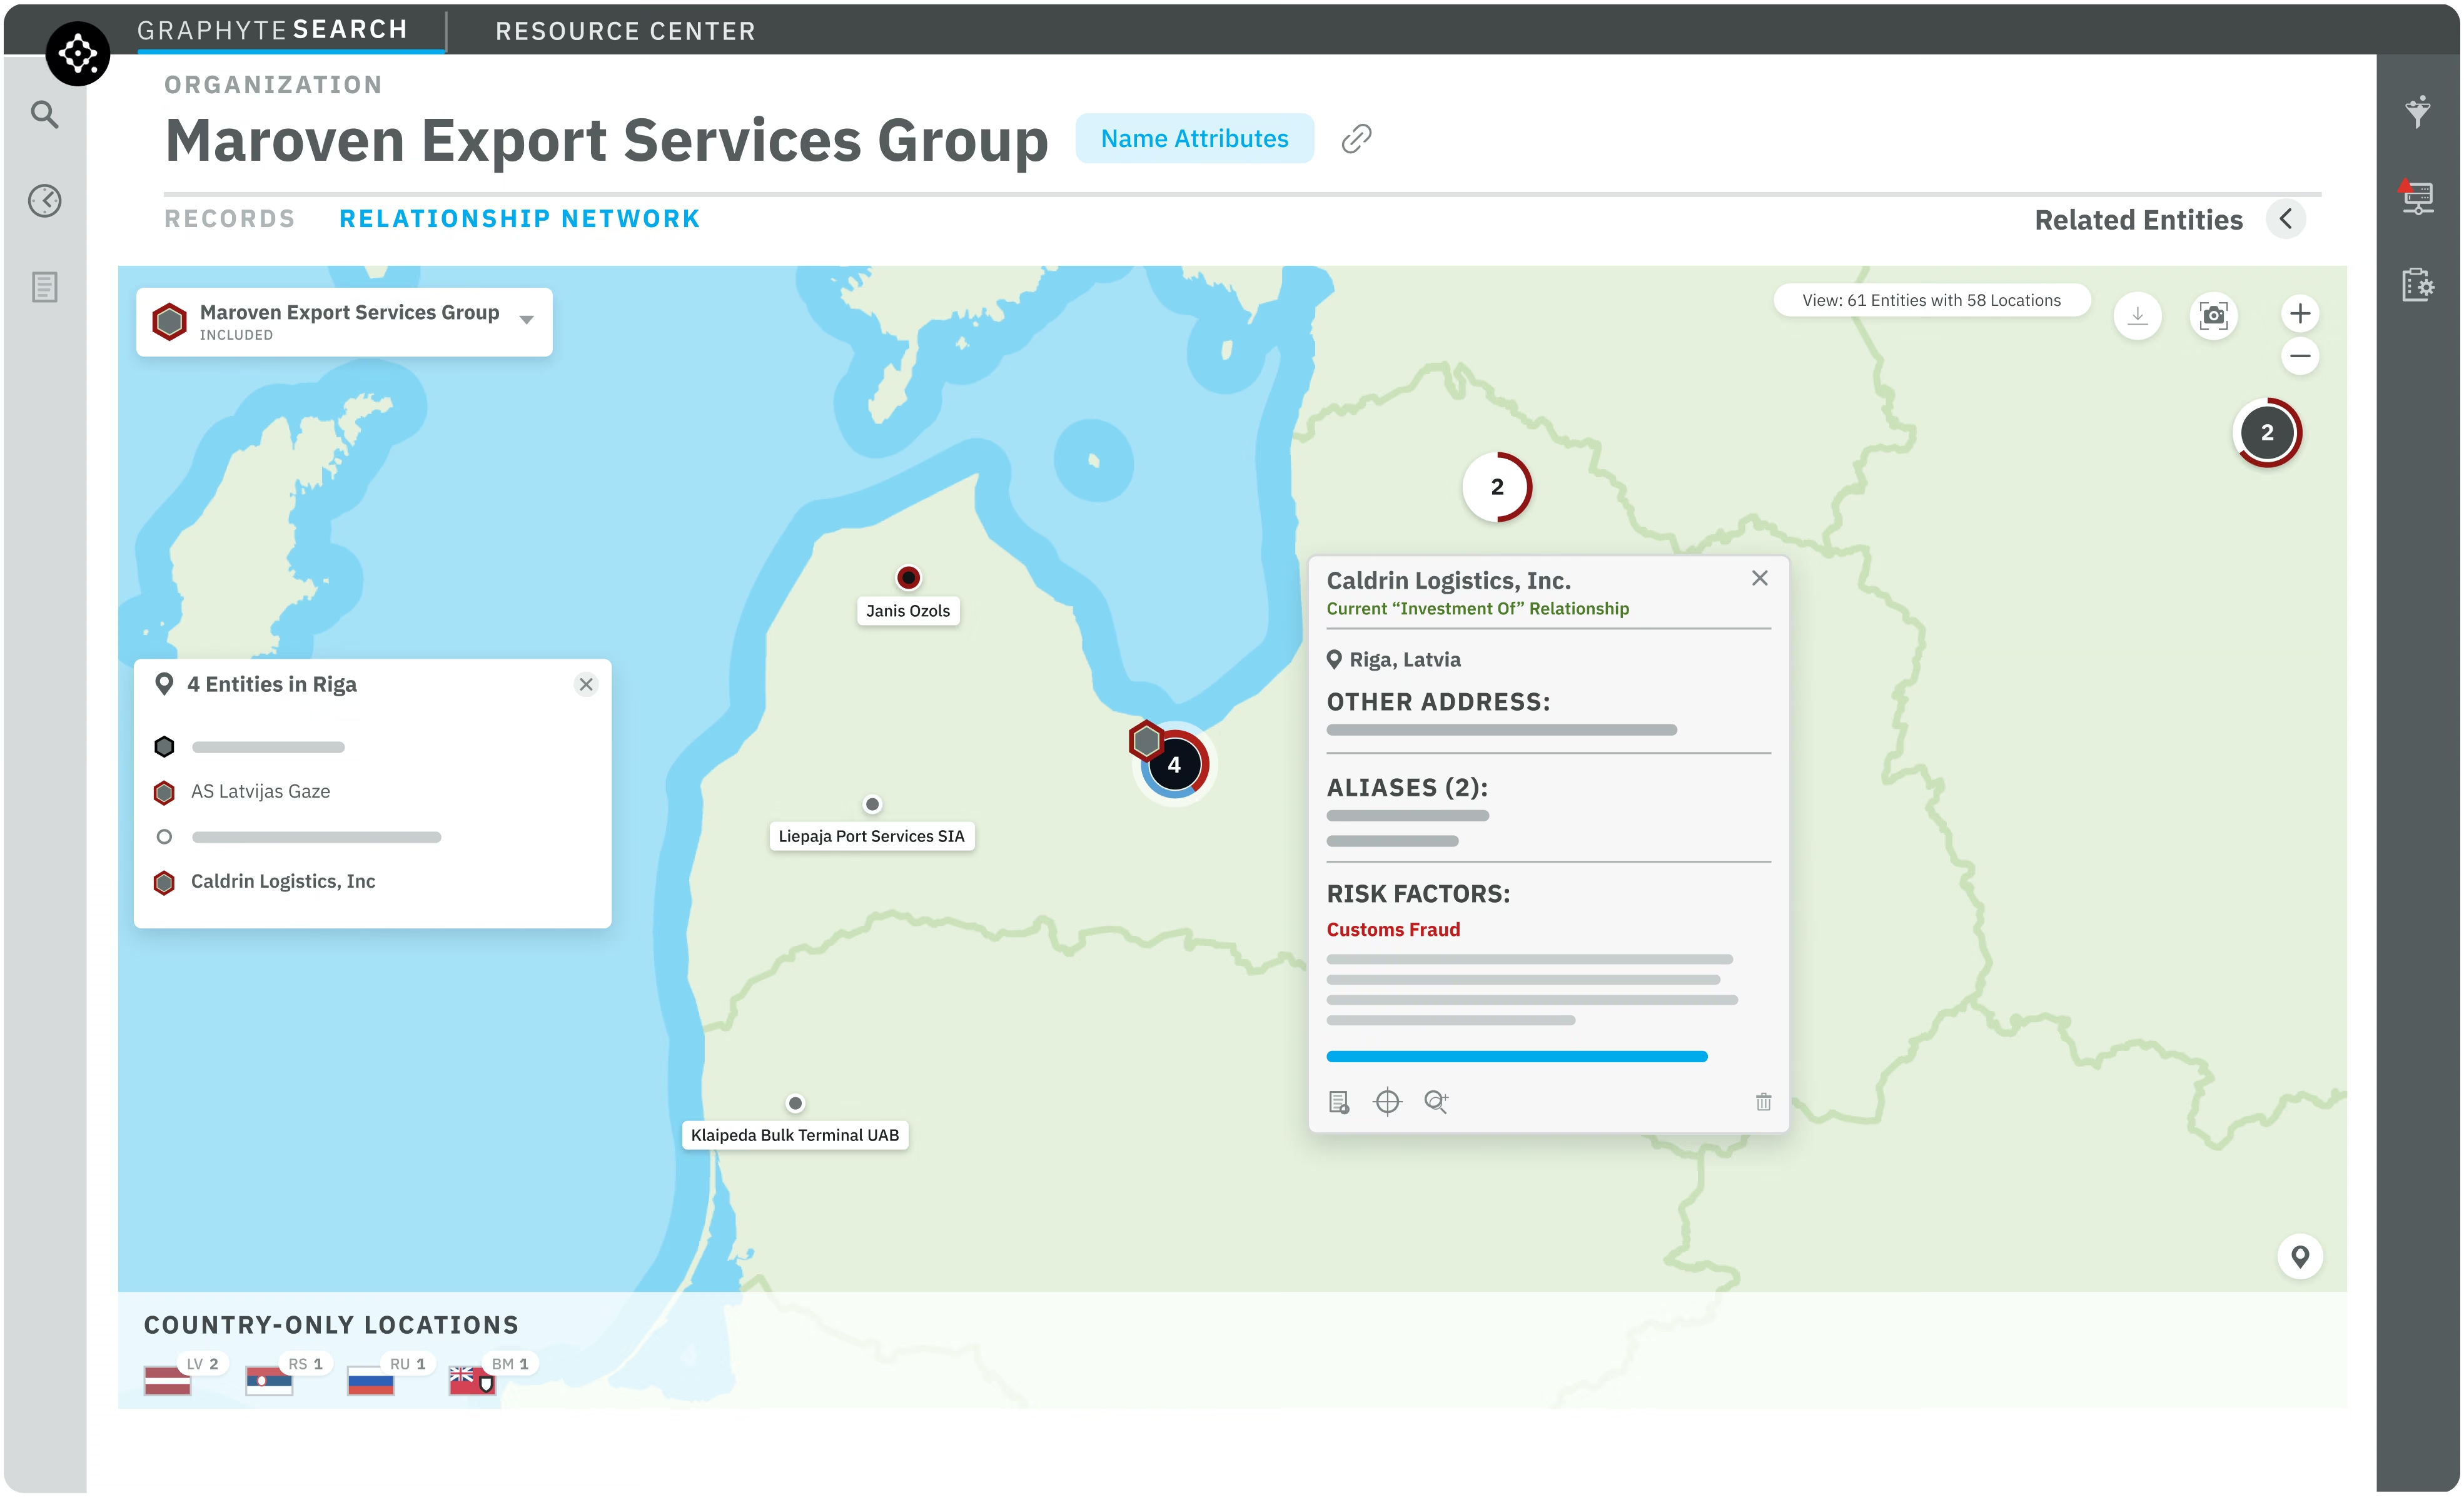
Automated network expansion maps ownership, investment, and subcontractor relationships through multiple degrees of separation, surfacing foreign ownership, control, or influence hidden behind shell companies and layers of subcontracting.
Adverse Media & Sanctions Screening
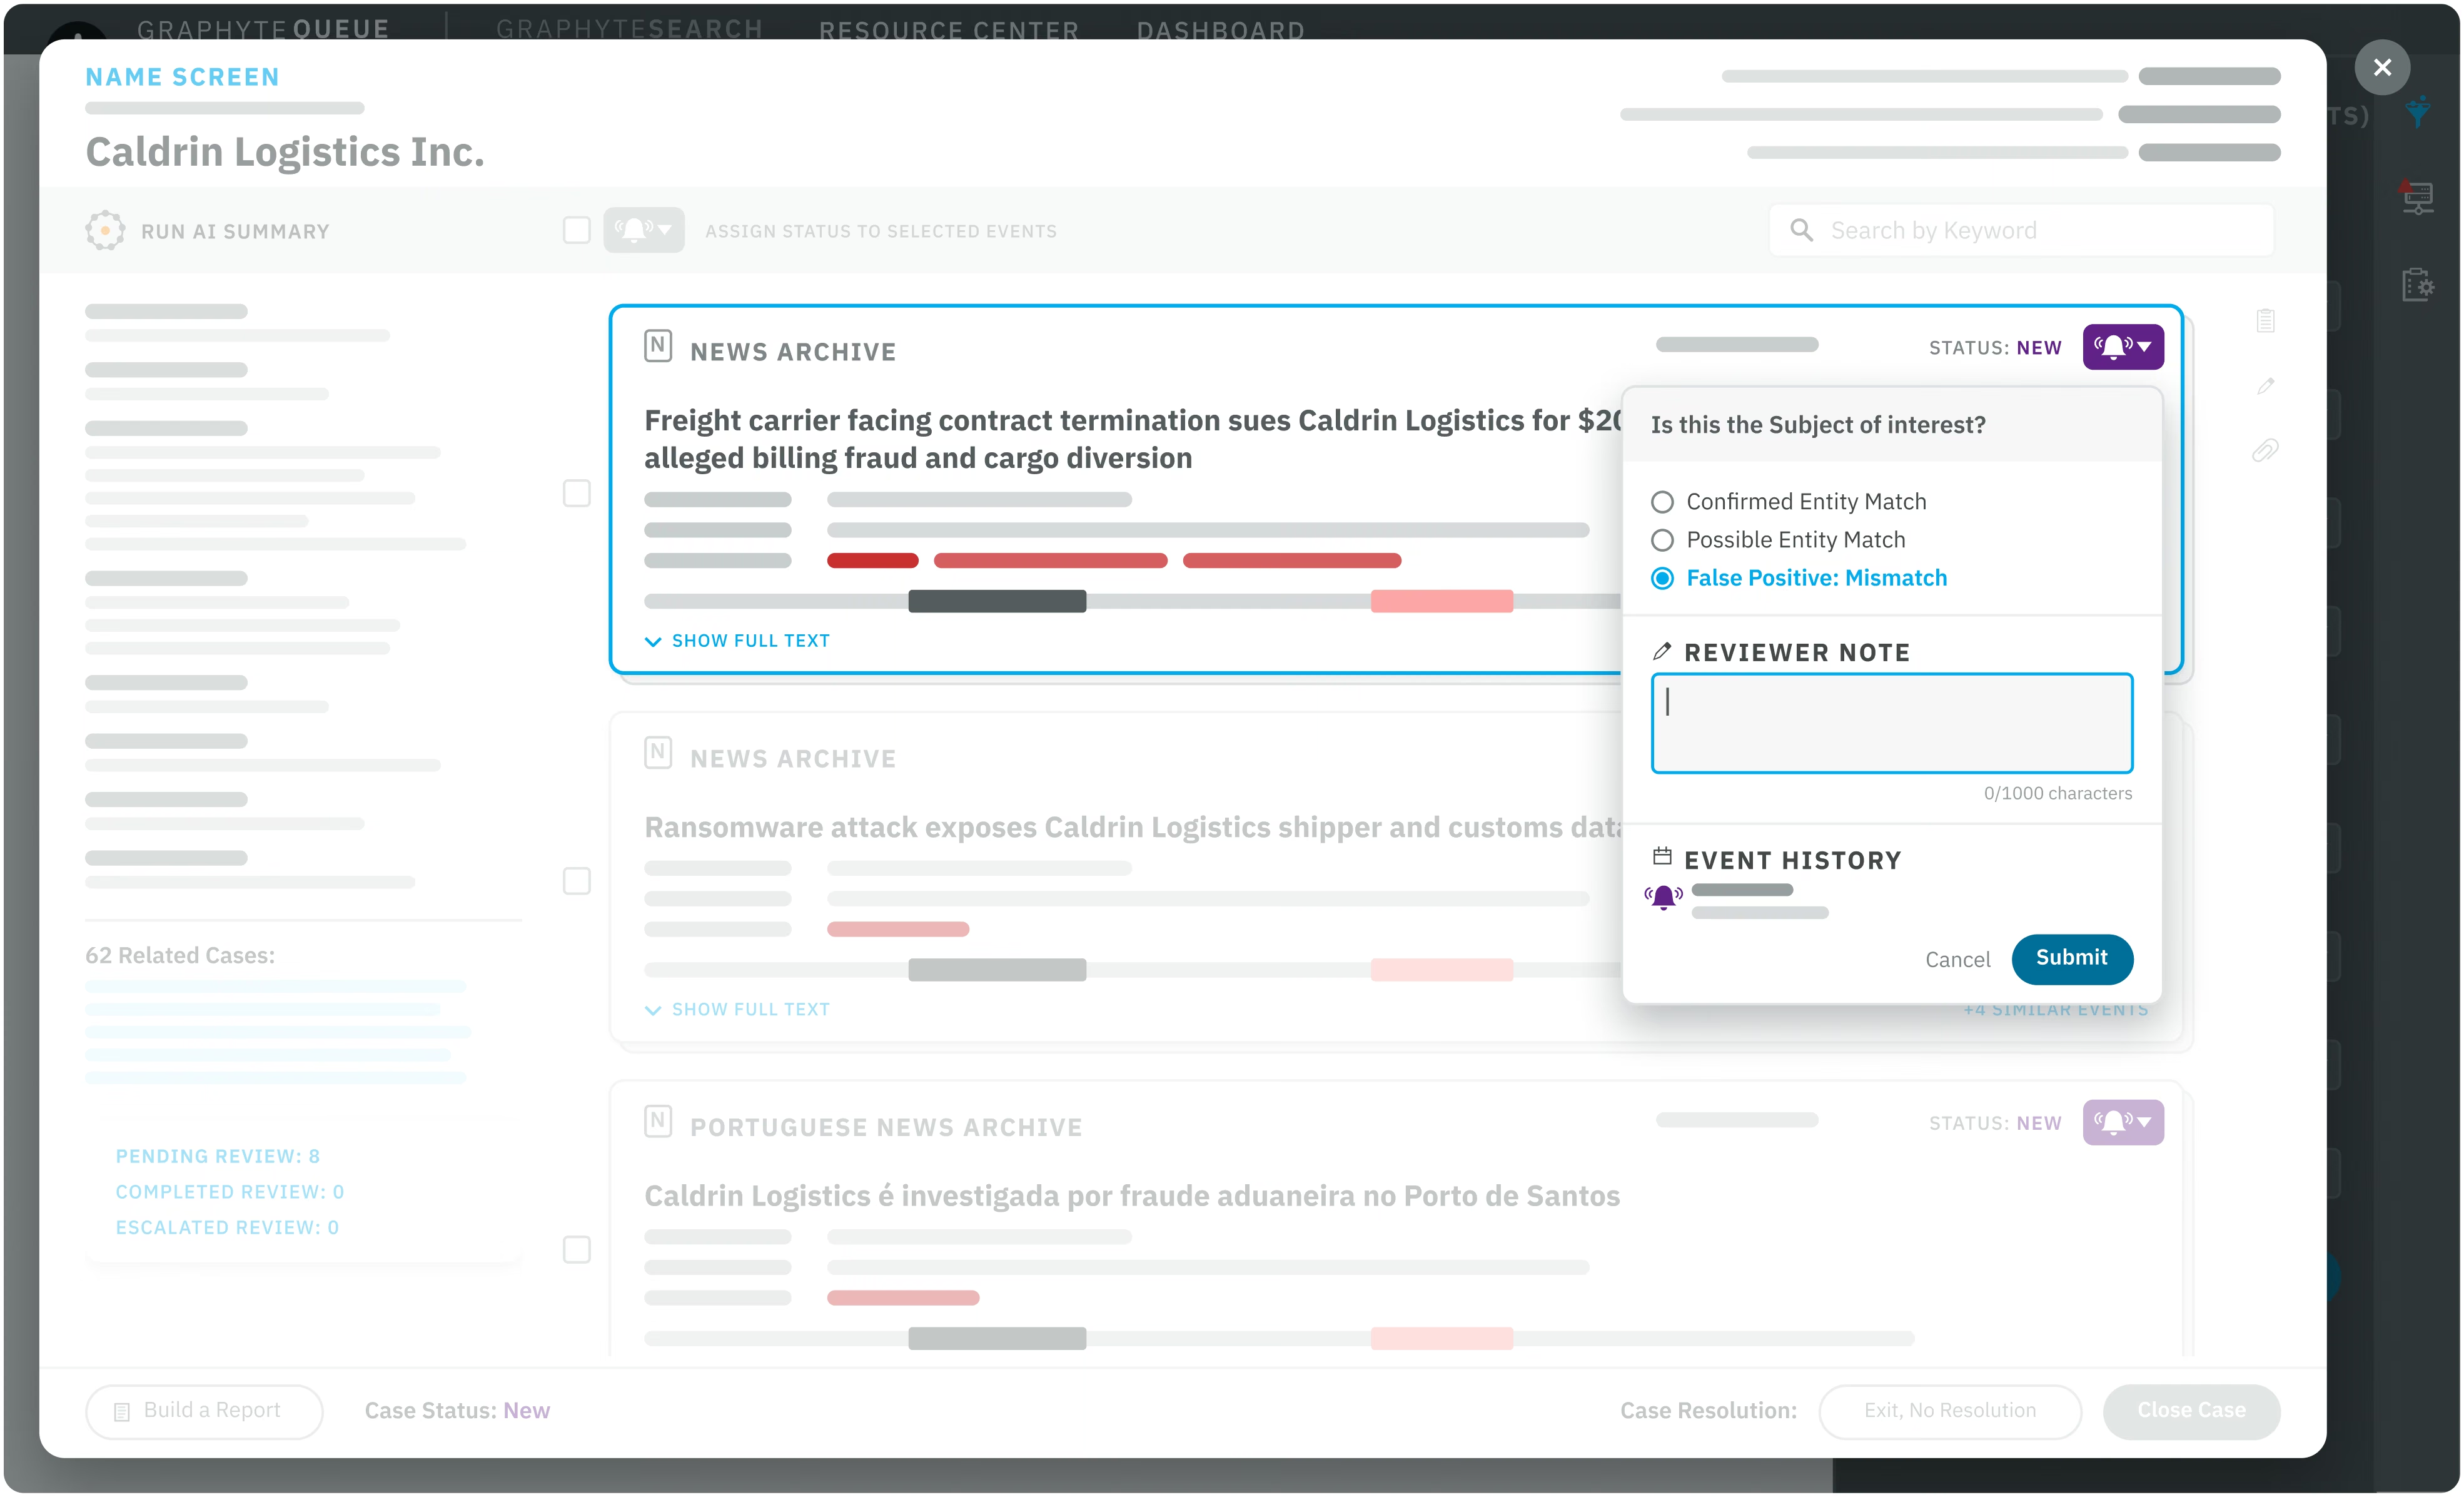
Risk extracted from a deep archive of global news and sanctions lists using dynamic risk typologies, not keyword hits, distinguishing a vendor's principal from an unrelated namesake or a passing mention.
Corporate & Trade Risk
Corporate registries across 130+ jurisdictions and global trade data expose ownership structures and trade-based risk behind a supplier.
Population-Scale Batch Screening
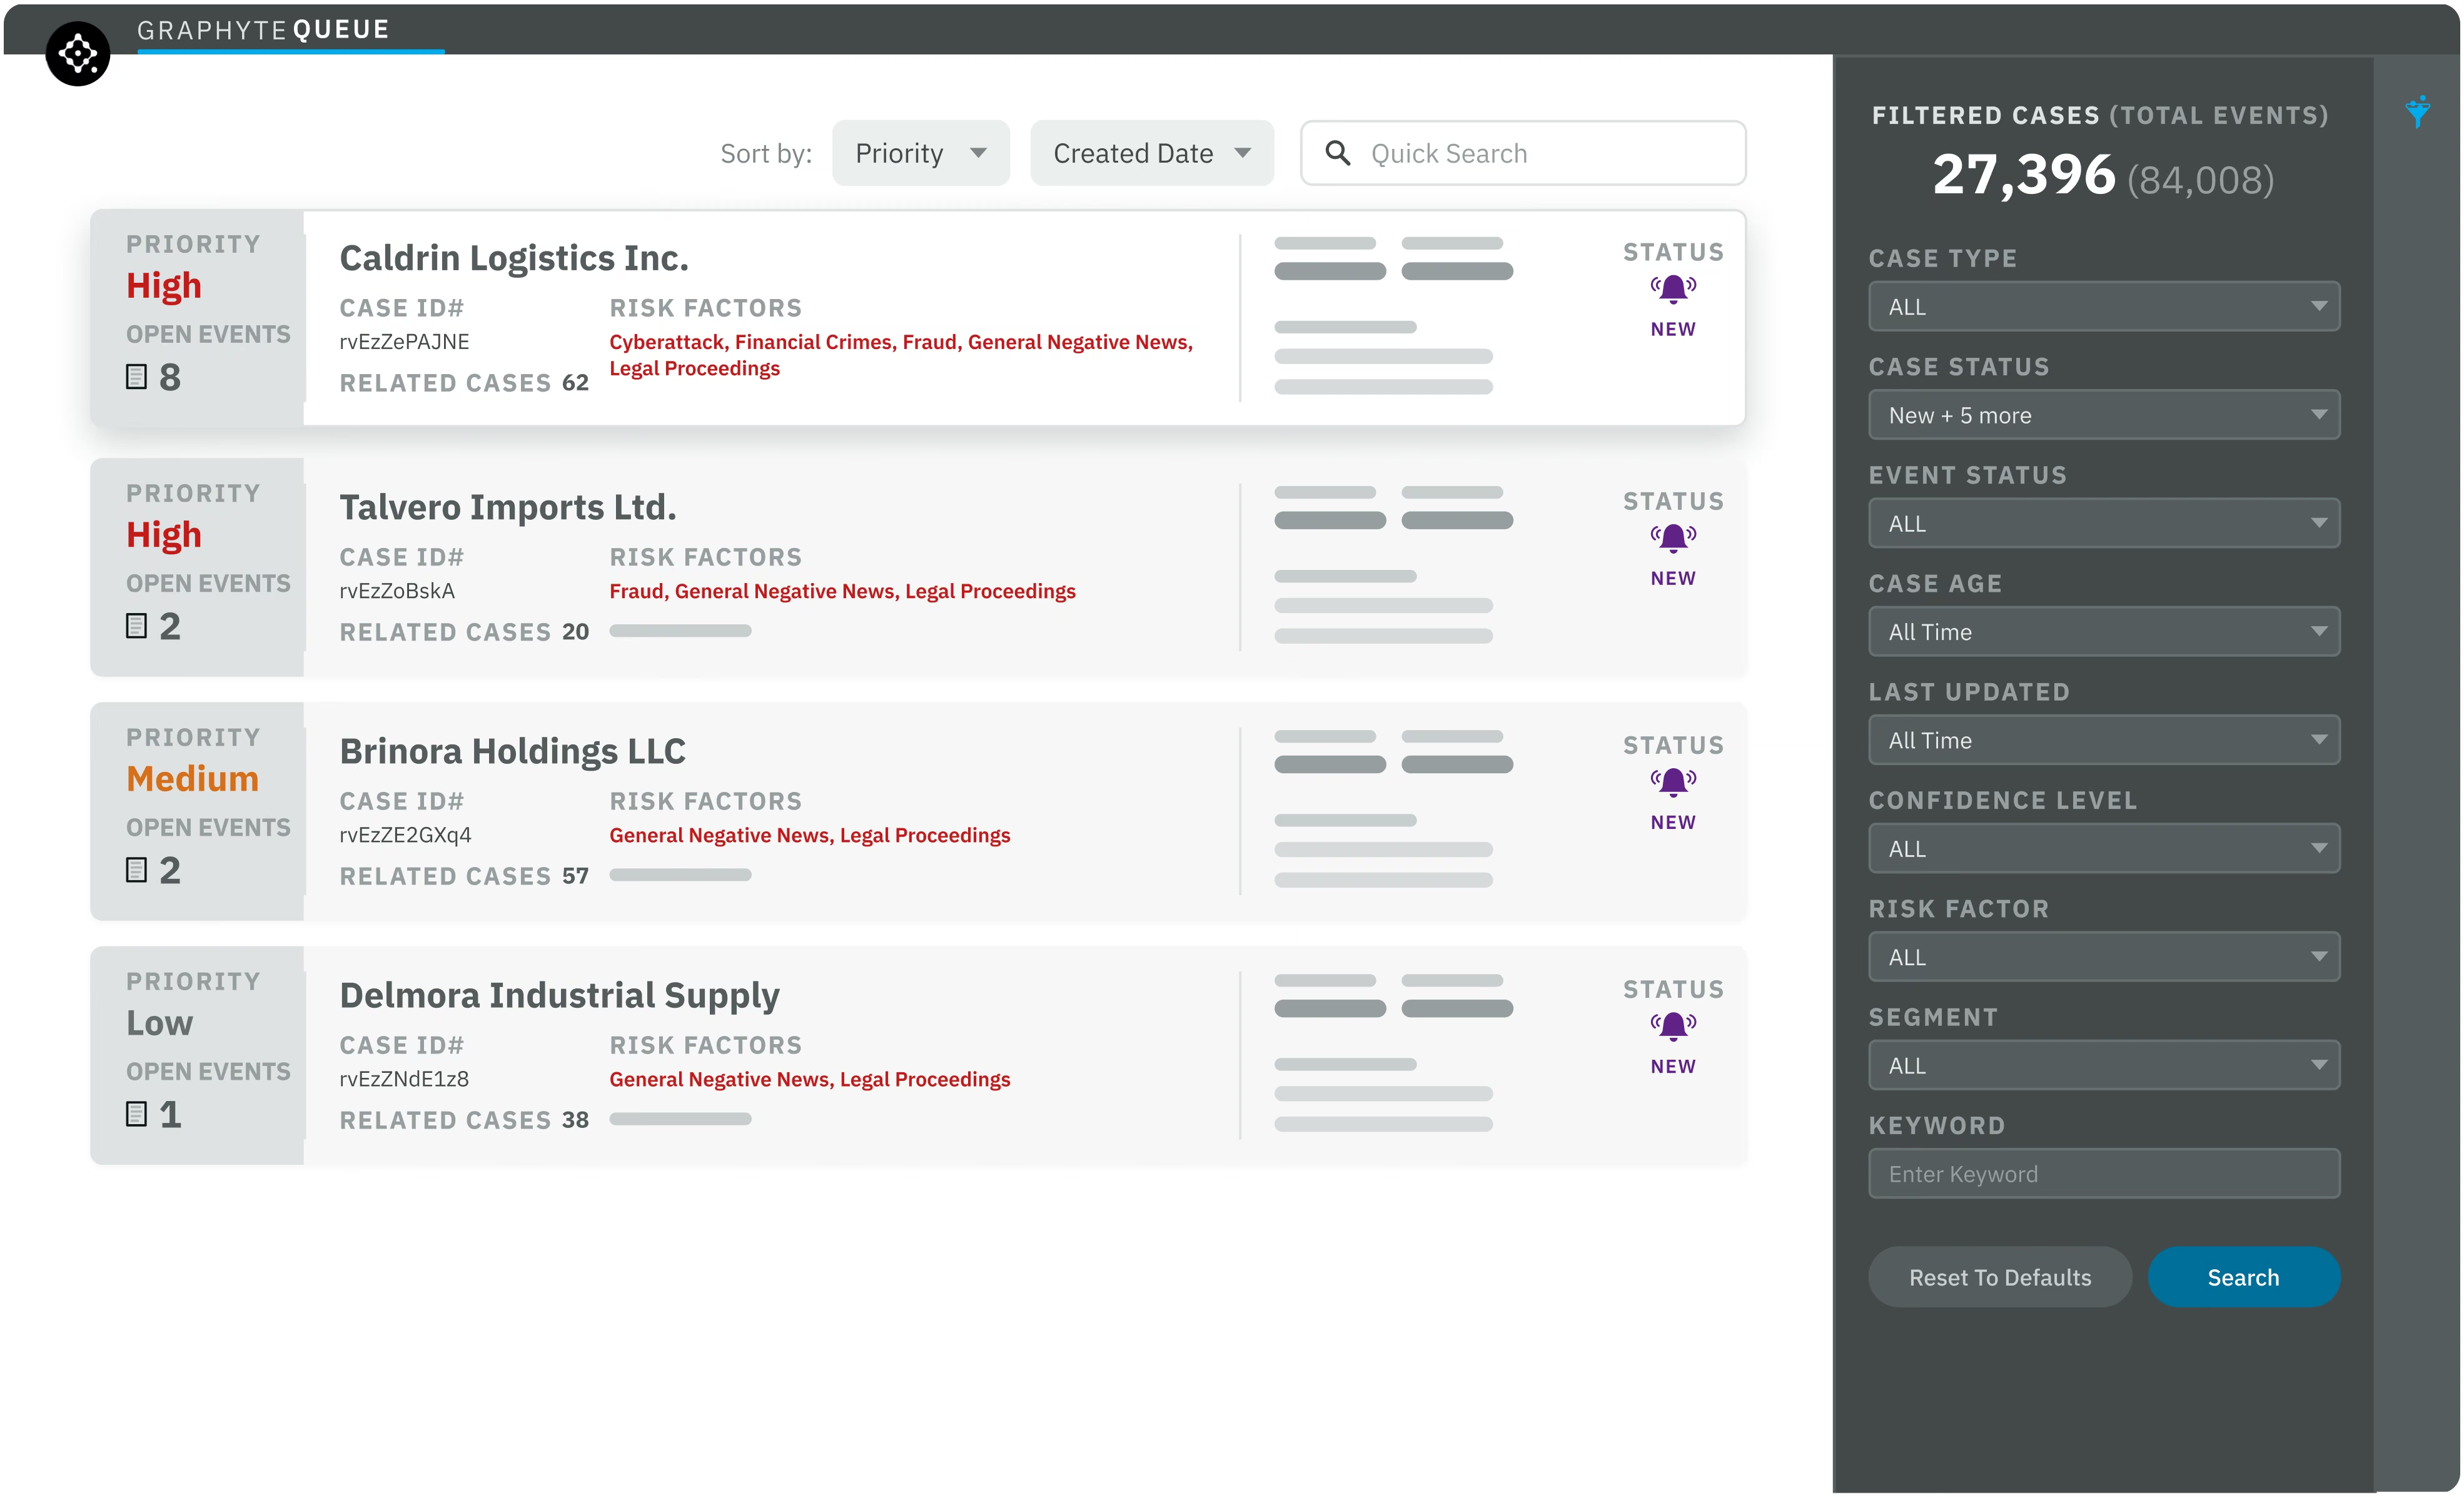
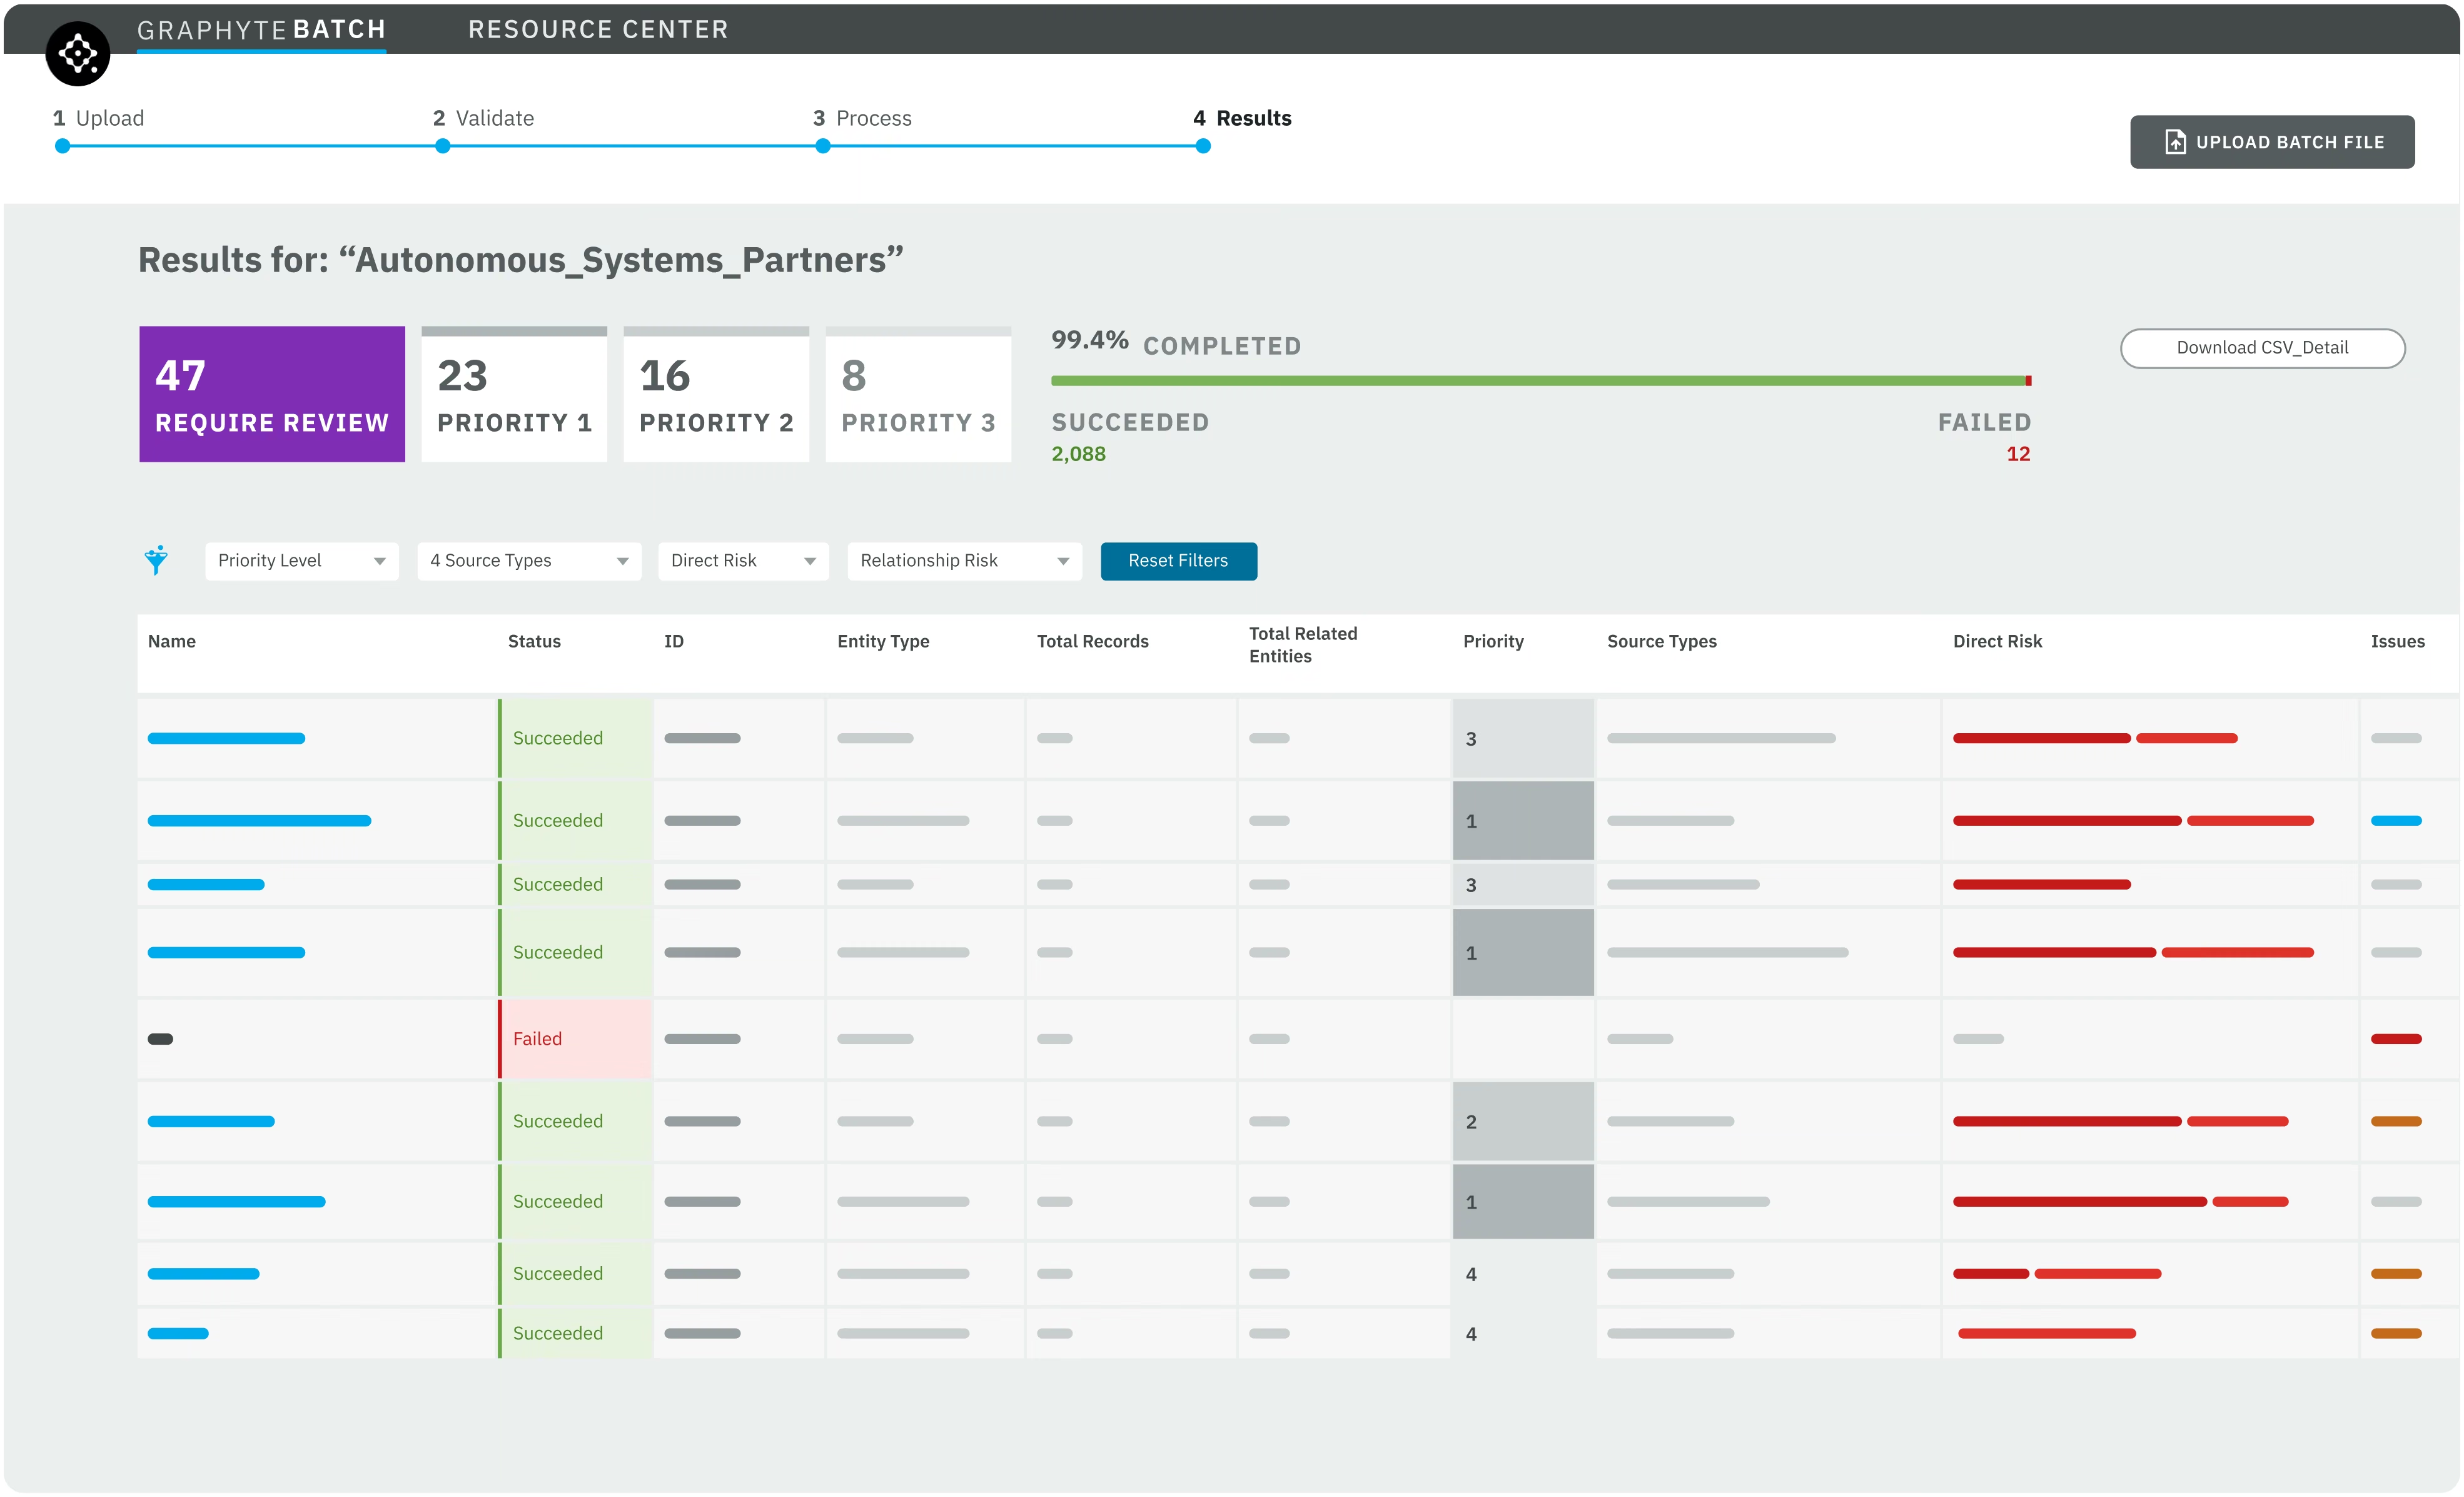
Screen an entire vendor registry, award file, or grantee list at once instead of one record at a time, giving small teams full population coverage during onboarding, recompete, and periodic re-review.
Audit-Ready Case Documentation
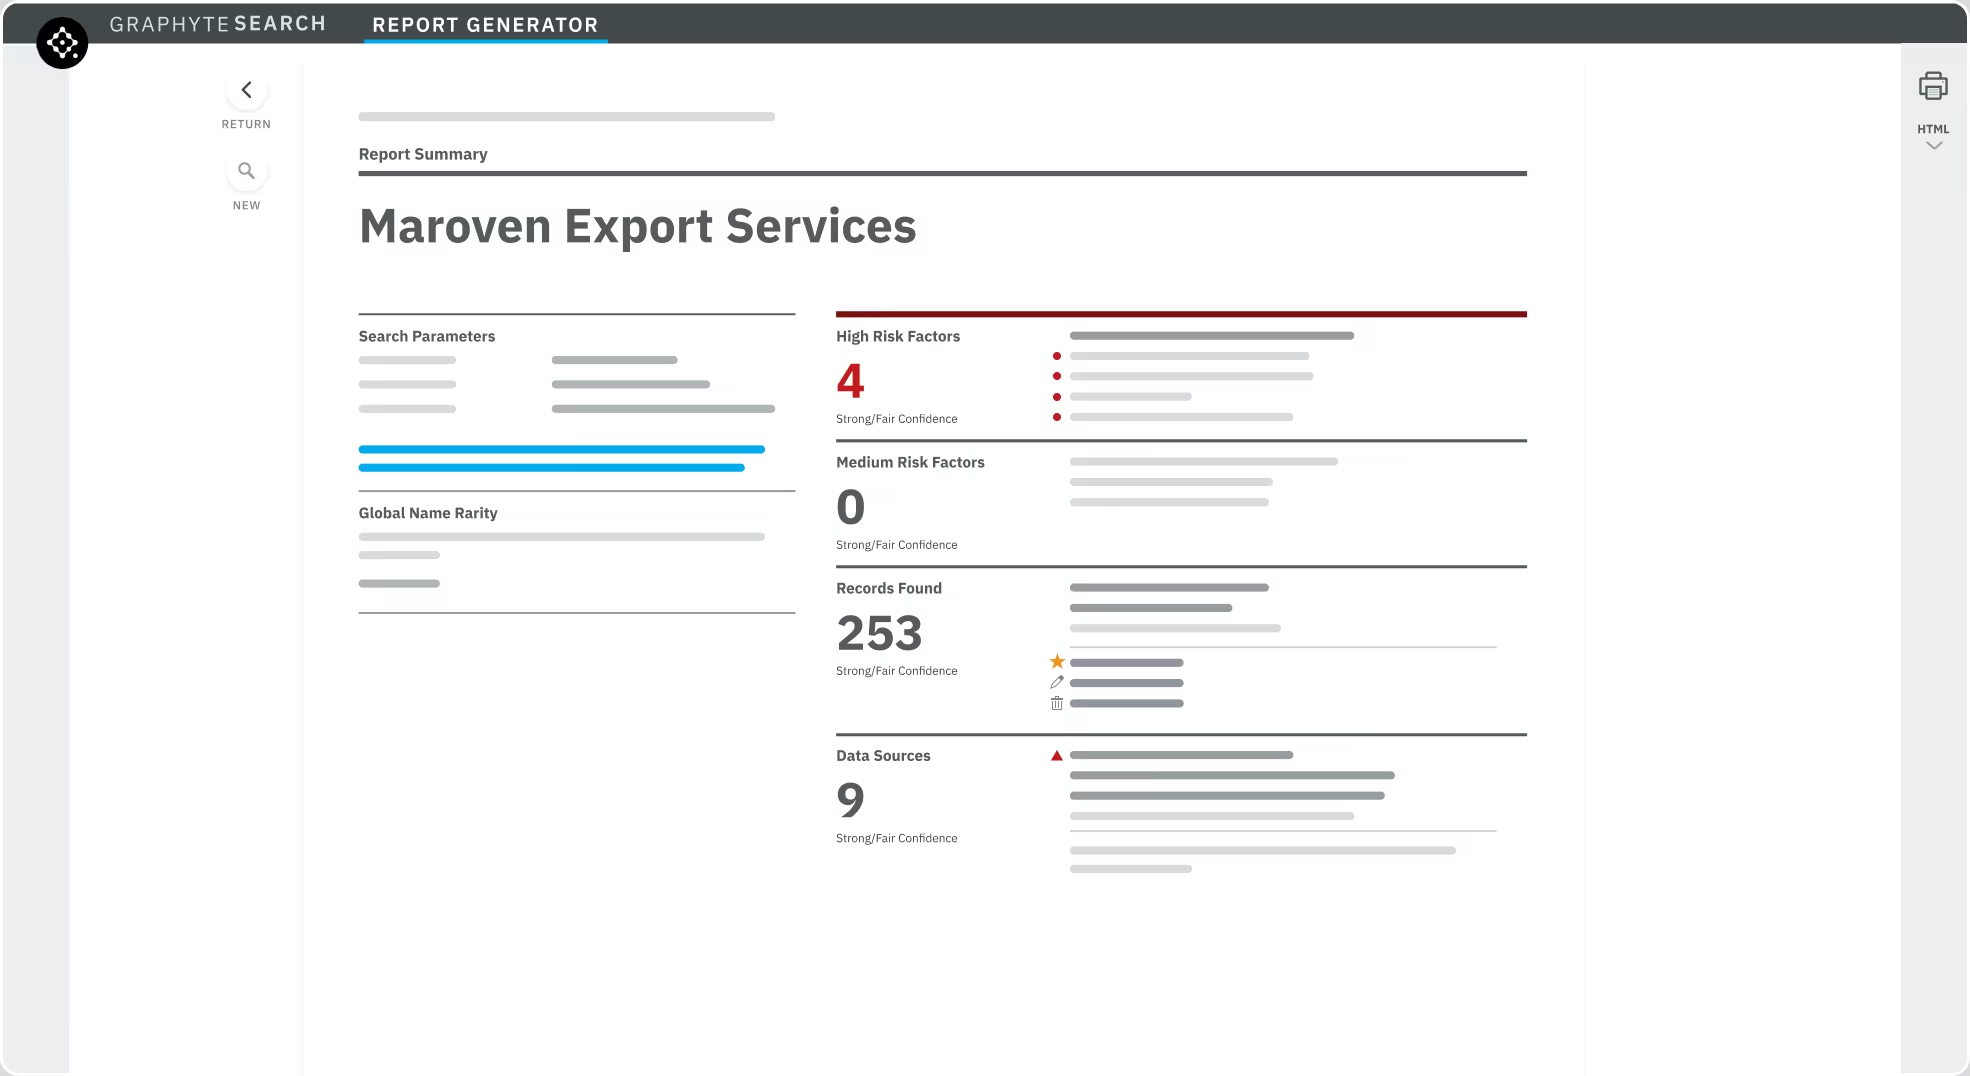
Every risk determination carries source evidence, confidence scoring, and a full chain of custody, ready for the acquisition record or an oversight review.
HOW IT WORKS
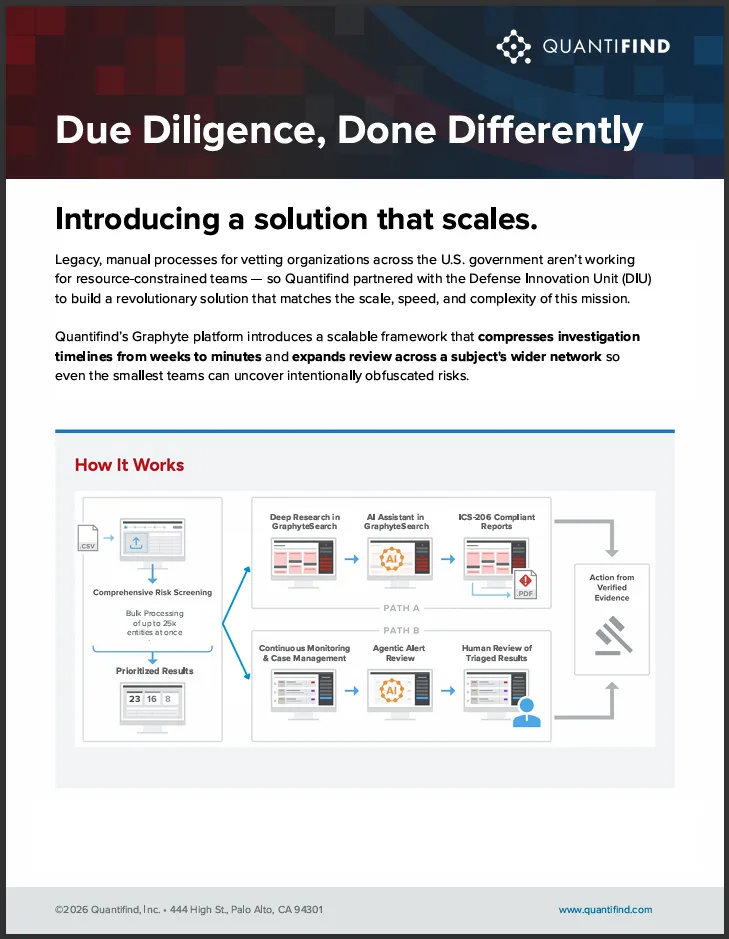
Go from a name to intelligence you can act on.
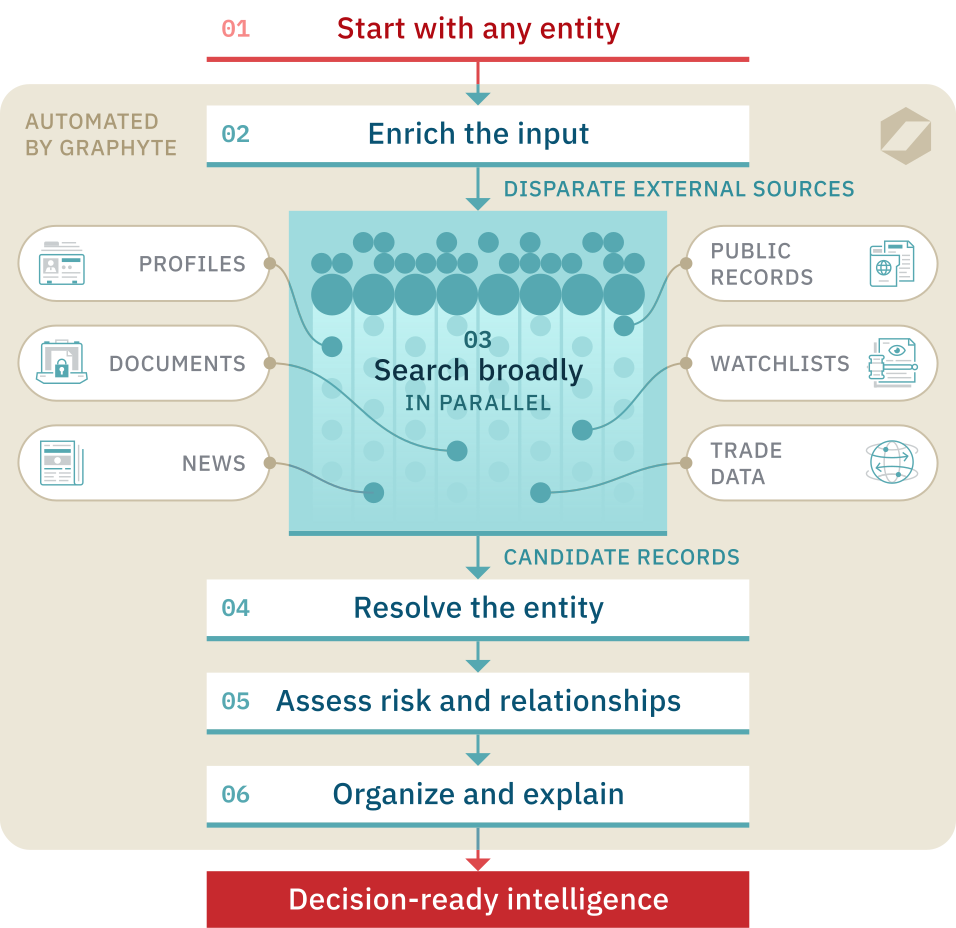
Start with an entity.
Initiate your search with as little as an individual name, organization, address, handle, email, or phone number. Search a single name, a vendor list, award file, or a public-database.
Contextualize and Search
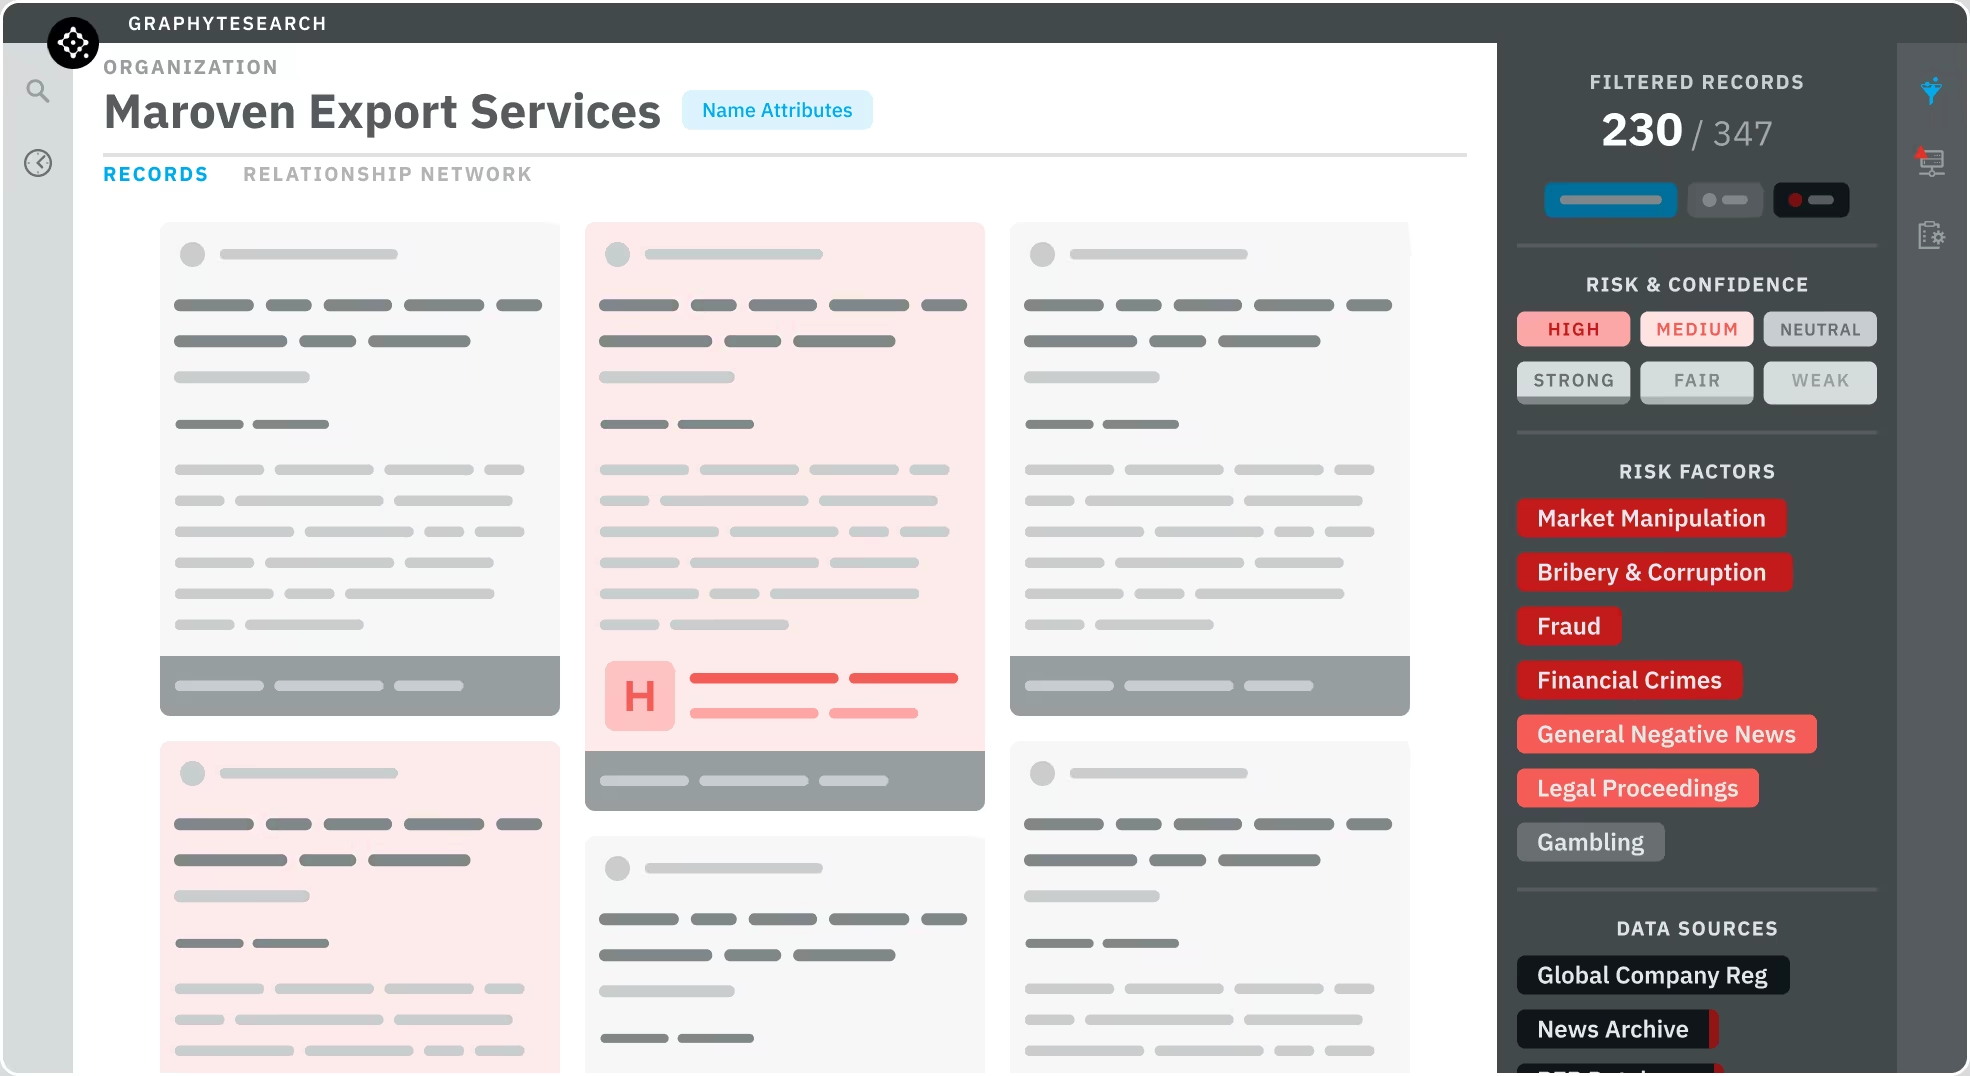
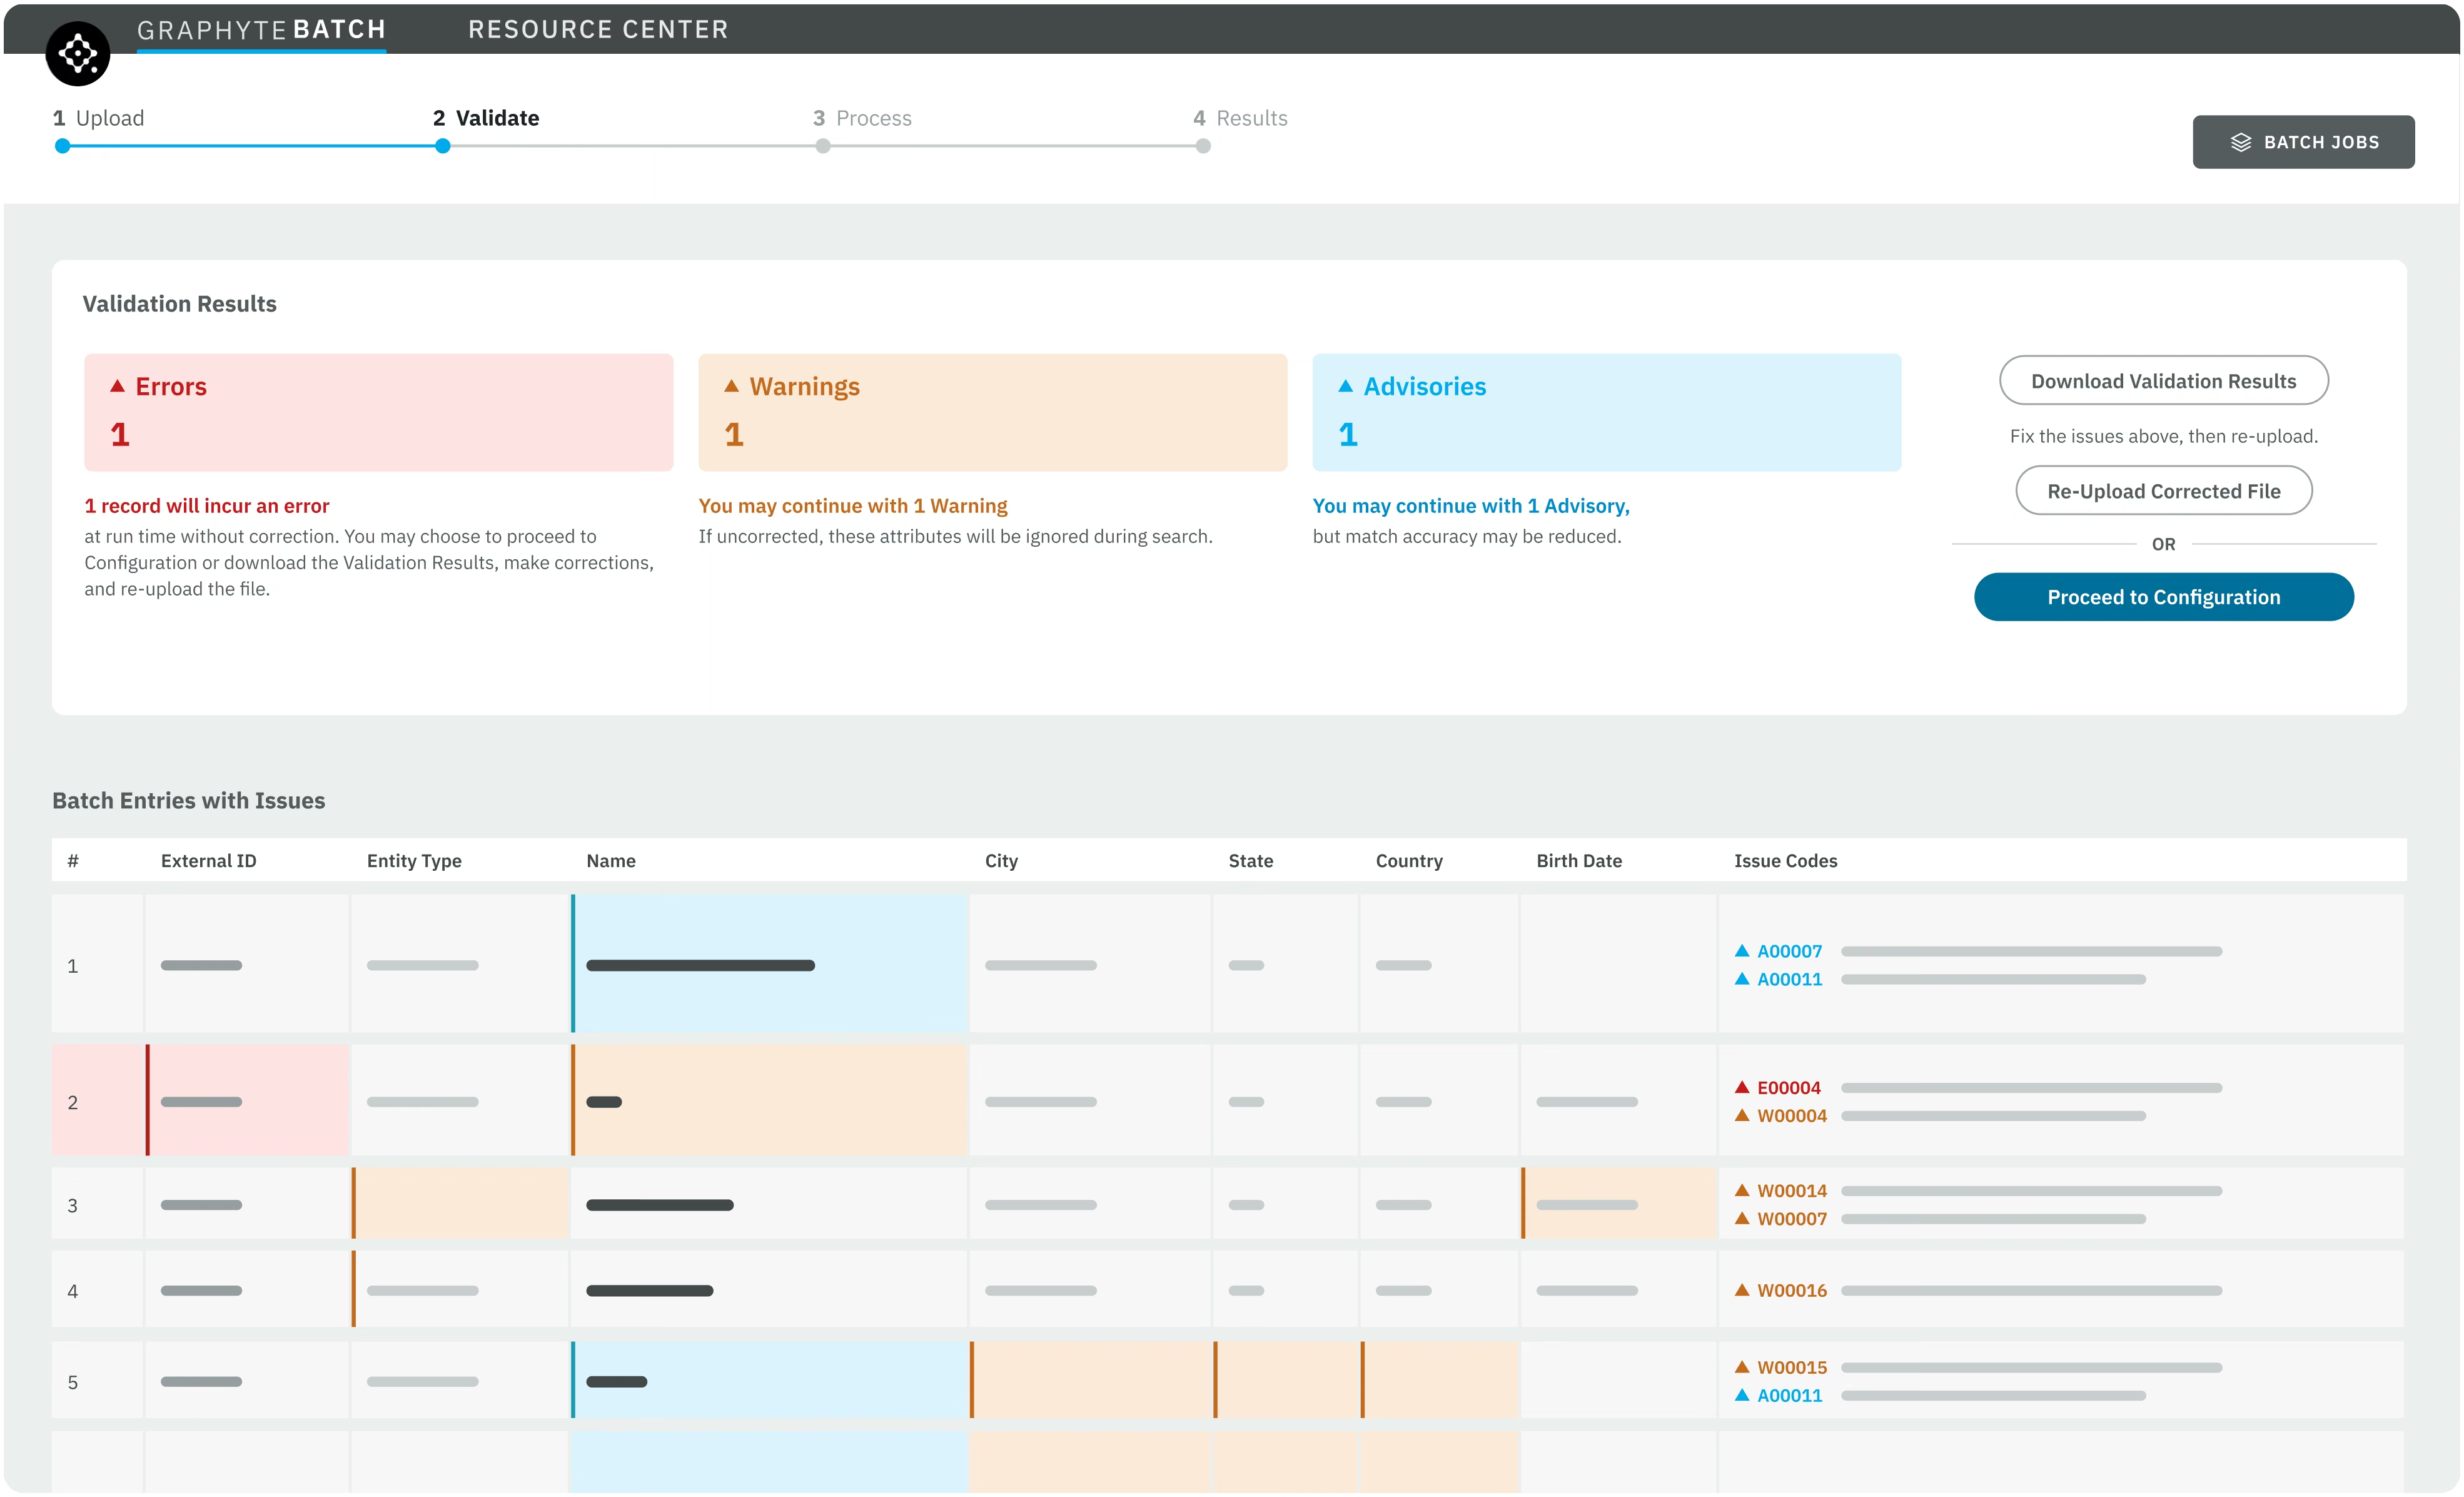
Graphyte standardizes the name and location, flags potential data quality issues, and adds linguistic context, expected name variations, and geographic precision, then scans 200+ global structured and unstructured data sources.
Resolve and Infer
Name Science™ and proprietary agentic middleware distinguish true matches among messy, multilingual data, then assembles a unified, confidence-scored profile by risk typologies, relationships, and relevance.
Assess and Decide
Graphyte aggregates and summarizes the results, organizing findings by risk and confidence with supporting context, source evidence, and provenance. All that's left is deciding what risk you accept, what warrants a closer look, and what happens next.
Continuous Monitoring
Continuous monitoring re-screens a fixed population against new data as it is ingested, replacing one-time checks or periodic re-screening. New risk signals, from a sanctions listing to a change in ownership, surface as they emerge, so you’re never the last to know.
“For the Defense Innovation Unit, Graphyte compresses foreign-affiliation screening from weeks to minutes, at a scale manual review cannot match.”
Frequently Asked Questions
Diligence software, answered.
What is due diligence software?
Government due diligence software helps procurement, compliance, and investigations teams vet vendors, contractors, and counterparties before and after award. Quantifind's Graphyte platform supports this work by resolving risk information to the correct entity, surfacing foreign ownership, control, or influence (FOCI) concerns, and helping teams document decisions for the record.
How does Graphyte support FOCI mitigation as part of a supply chain risk management solution?
Graphyte maps ownership and investment structures, subcontractor relationships, and component sourcing to uncover supply chain and ownership risks that might otherwise go unnoticed. It combines best-in-class AI-powered entity resolution with knowledge of over 60 expert-built risk typologies, tracing beneficial ownership; foreign ownership, control, or influence (FOCI); sanctions exposure, and dozens of other risk factors across multi-tier vendor networks. This helps procurement and compliance teams identify customers and counterparties tied to elevated risk exposure before those relationships become a liability.
What data sources does Graphyte screen for government due diligence?
Graphyte draws on corporate registries across 130+ jurisdictions, sanctions and watchlists, global trade data, legal and regulatory records, and global news and adverse media in 9 languages. That information is resolved to the correct entity and evaluated in context as part of a broader risk assessment, enabling third party due diligence on vendors, subcontractors, and grant recipients that a single-source check would miss.
Can Graphyte screen large vendor and contractor networks at scale?
Yes. Graphyte supports bulk and batch screening, allowing teams to vet large populations of vendors, subcontractors, and grantees at once rather than one record at a time. This lets small teams cover more ground during onboarding, recompete, and periodic re-review without adding headcount.
Can Graphyte help satisfy FAR and DFARS supply chain risk requirements?
Yes. FAR and DFARS provisions increasingly require contracting officers and prime contractors to assess foreign ownership, control, or influence and broader supply chain risk before and during award. Graphyte supports that work by resolving vendor and subcontractor entities, mapping ownership and component sourcing across multiple tiers, and surfacing FOCI, sanctions, and other risk factors with source-linked evidence teams can document for the acquisition record.